Safeguarding Critical Infrastructure: Essential Cybersecurity Strategies for Industrial Control Systems (ICS)
- 〡
- 〡 by WUPAMBO
The Evolution of Industrial Control Systems and Modern Vulnerabilities
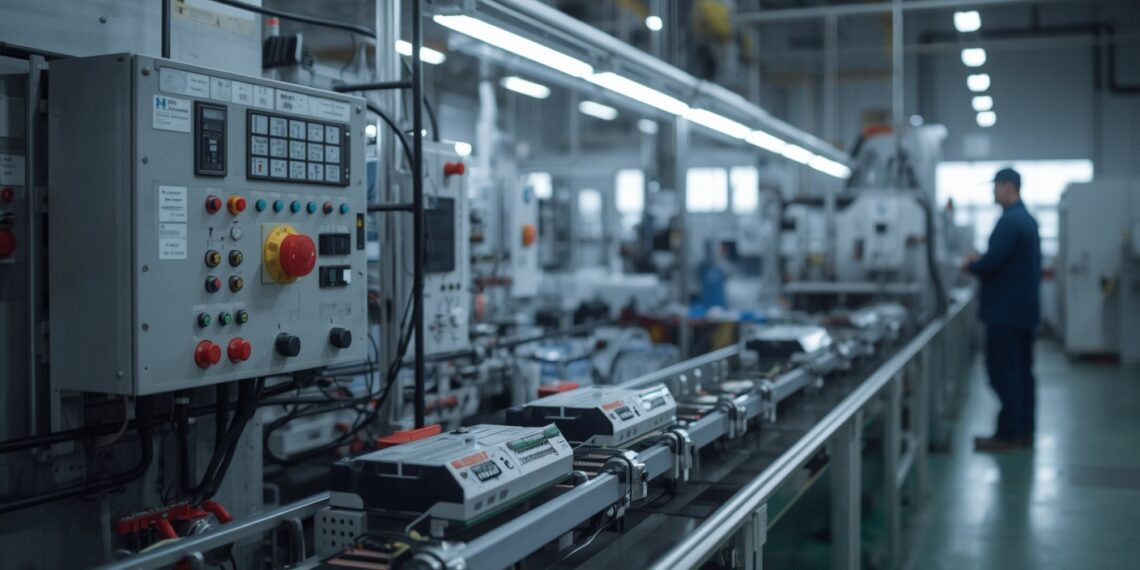
Industrial control systems govern critical infrastructure worldwide. Traditionally, these systems operated in complete isolation from corporate networks. Engineers utilized proprietary control protocols and specialized hardware to maintain plant safety. However, modern facilities now integrate low-cost Internet Protocol devices and commercial operating systems. As a result, factory automation networks closely resemble standard information technology environments.
This digital transformation brings unprecedented operational efficiency. Furthermore, it introduces significant cybersecurity vulnerabilities. External adversaries can now exploit connected networks, threatening physical plant operations and human safety.
Unique Security Objectives in Control Systems
Industrial environments prioritize security objectives differently than standard IT infrastructures. In factory automation, system availability and data integrity always take precedence over confidentiality.
When cyber incidents strike, they directly impact the physical world. For example, malicious actors can manipulate programmable logic controllers to disrupt production or damage expensive machinery. Therefore, comprehensive cybersecurity programs must protect human lives, prevent environmental disasters, and safeguard national economies.
Implementing Defense-in-Depth Strategies for ICS Security
Robust industrial security requires a layered defense strategy. Organizations must never rely on security through obscurity. Instead, security teams should implement a comprehensive framework across the entire asset lifecycle:
- Network Segregation: Deploy stateful inspection firewalls and demilitarized zones to separate corporate networks from critical control networks.
- Access Control: Enforce strict role-based access control and mandate multi-factor authentication for all operators.
- Vulnerability Management: Test security patches rigorously in offline environments before deploying them to live production lines.
- Continuous Monitoring: Maintain active audit trails and deploy intrusion detection systems specifically tailored for industrial protocols.
As an automation expert, I strongly recommend conducting regular penetration testing on legacy distributed control systems to uncover hidden vulnerabilities before malicious actors exploit them.
Cross-Functional Cybersecurity Governance
Securing modern manufacturing plants demands cross-functional collaboration. Plant managers cannot manage industrial cybersecurity alone. Instead, organizations must establish dedicated teams consisting of IT professionals, control engineers, system operators, and physical security experts.
Moreover, chief information officers must accept full accountability for any safety incidents caused by cyber breaches. Collaboration with system integrators further ensures that security measures do not interfere with real-time process execution.
Practical Application Scenario: Securing a Water Treatment Facility
Consider a municipal water treatment plant migrating to a smart SCADA architecture. The facility utilizes distributed control systems and programmable logic controllers to regulate chemical dosing.
To prevent unauthorized remote tampering, engineers implement unidirectional security gateways and zone-based network segmentation. Furthermore, they disable all unused physical communication ports on every controller.
During pre-commissioning testing, the security team simulates a denial-of-service attack. The system responds smoothly by initiating graceful degradation protocols, switching critical loops to manual operation without interrupting water delivery. Consequently, the facility achieves total compliance with critical infrastructure protection standards.
Author Biography
The author, Chen Bo, is a senior industrial automation and control systems specialist with 15 years of field experience. He has served as a lead security architect for major smart manufacturing and critical infrastructure projects across the globe. Chen specializes in industrial network security, PLC programming, and distributed control system migration. He regularly publishes technical insights to help engineers bridge the gap between traditional factory automation and modern cybersecurity standards.
- Posted in:
- control systems
- critical infrastructure protection
- DCS
- defense in depth
- factory automation
- ICS cybersecurity
- PLC
- SCADA security